OutSystems aims to protect all forms of information with improved resilience, thereby creating lasting relationships that guarantee customer success. To that end, OutSystems has implemented an Integrated Management System for Quality, Information Security, and Business Continuity, in the scope of OutSystems Support services, in its offices located in the U.S., Portugal, Japan, and Malaysia.
As part of our commitment to security best practices in cloud computing, OutSystems is a member of the CSA. In addition, we have completed the CSA STAR Self-Assessment and published the results to their website.
Table of contents
OutSystems holds a long list of certifications that can be consulted at all times in the dedicated OutSystems Trust Center, including these standouts:
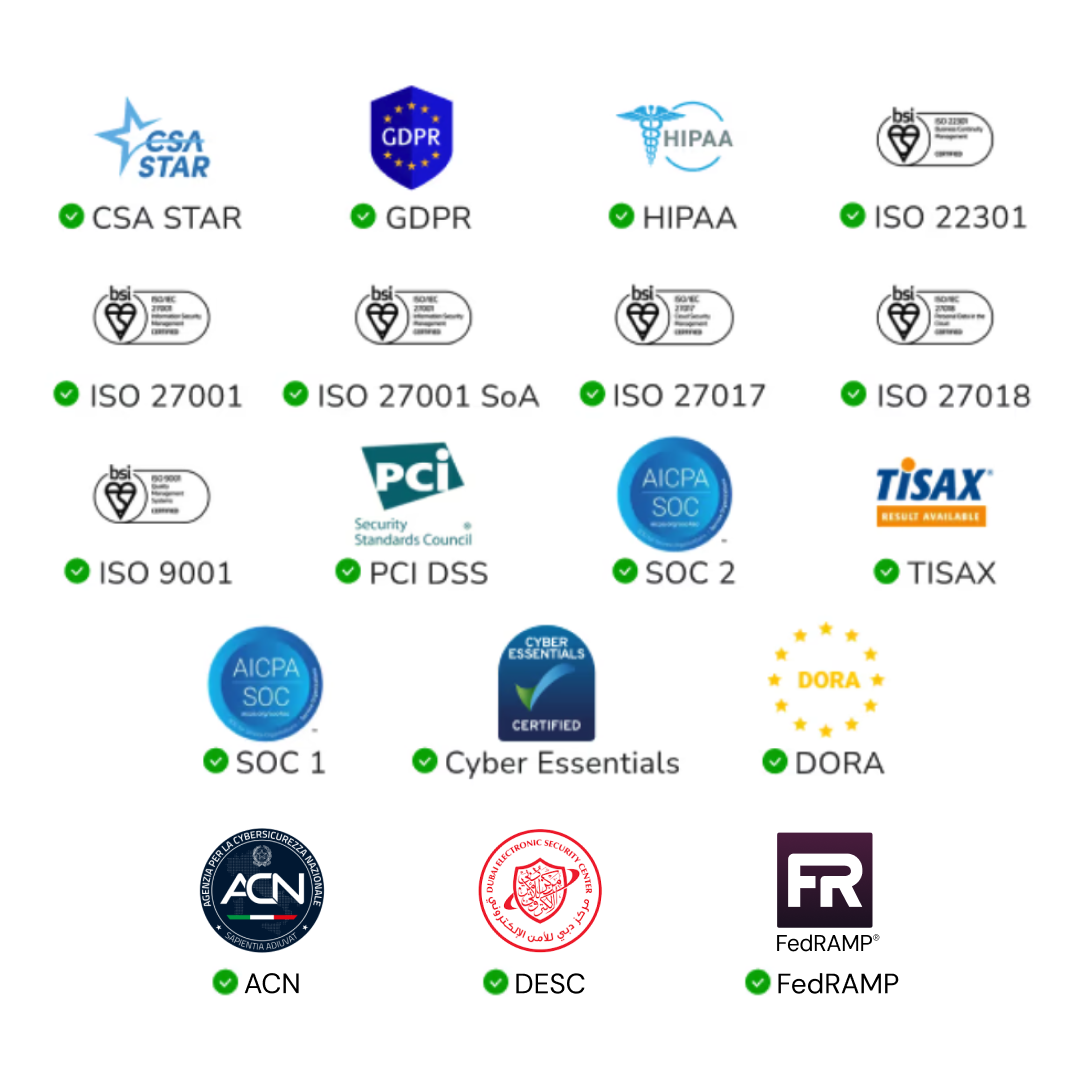
OutSystems maintains compliance with the following industry standards and regulations.
The OWASP Top 10, OWASP Low Code Top 10 and OWASP Mobile Top 10 represent a broad consensus on the most critical security risks to web and mobile applications. Consult our technical documentation for more information on how applications built with OutSystems are safeguarded against the security liabilities identified by OWASP.
OutSystems Center for Internet Security (CIS) membership provides access to assessment tools, compliance benchmarking, and reporting capabilities, enabling us to incorporate the latest security protections into our platform. It also allows us to monitor internal technologies and customer cloud-based systems for compliance, ensuring a proactive and adaptable cybersecurity approach. CIS Benchmarks™, an important component of CIS SecureSuite, are recommended as industry-accepted system hardening standards. These standards are used by organizations as guidance for meeting compliance requirements mandated by industry or government entities. Access to these standards continuously helps OutSystems build and update its platform with the latest configurations and best practices for cybersecurity.
OutSystems adheres to the AWS Foundations and Well-Architected framework, providing additional reassurance for applications built with our platform. The adoption of this framework safeguards that infrastructures are built securely and are high-performing, resilient, and efficient for a variety of applications and workloads. It also provides customers with additional clarity about the roadmap for designing and running applications in the cloud, helping them avoid common pitfalls and staying ahead of potential security issues.
OutSystems ensures platform integrity through a continuous cycle of independent third-party audits, comprehensive vulnerability management, and penetration tests. This multi-layered approach validates our operational controls, infrastructure security, and data handling procedures against evolving threats. By maintaining rigorous internal oversight and external validation, we provide objective, verifiable assurance of our security posture.
Our global compliance framework is architected to meet stringent international, regional, and industry-specific regulatory requirements. We maintain a broad portfolio of certifications and attestations that cover data privacy, financial reporting, and specialized sector standards. This ongoing investment in rigorous validation minimizes the auditing and compliance burden for our customers, allowing teams to deploy applications with the confidence that the underlying infrastructure is secured to the highest global benchmarks.
OutSystems Security Operations Center (SOC) provides security monitoring services to protect OutSystems infrastructure from cyberattacks and the loss of its intellectual assets.
The primary mission of the OutSystems SOC is to help ensure company, system, and data preservation through comprehensive investigations into computer security incidents and to contribute to the prevention of such incidents. Therefore, it engages in proactive threat assessment, mitigation planning and incident trend analysis.
If a potential attack is reported, the OutSystems combined security teams and mechanisms take the following steps:
By implementing these measures, our goal is to swiftly detect and resolve security incidents, minimizing their impact on our customers' applications and data. Furthermore, the gathered information is used in dedicated feedback loops for in-depth post-mortem analysis and root cause identification, ensuring valuable insights are applied for future incident management.