エージェント型システムプラットフォーム
エンタープライズレベルのセキュリティとコンプライアンスを実現
OutSystemsは、プラットフォームとそのアプリケーションのあらゆる側面に最新のエンドツーエンドのセキュリティが組み込まれた、開発に安心感をもたらすエージェント型システムプラットフォームです。
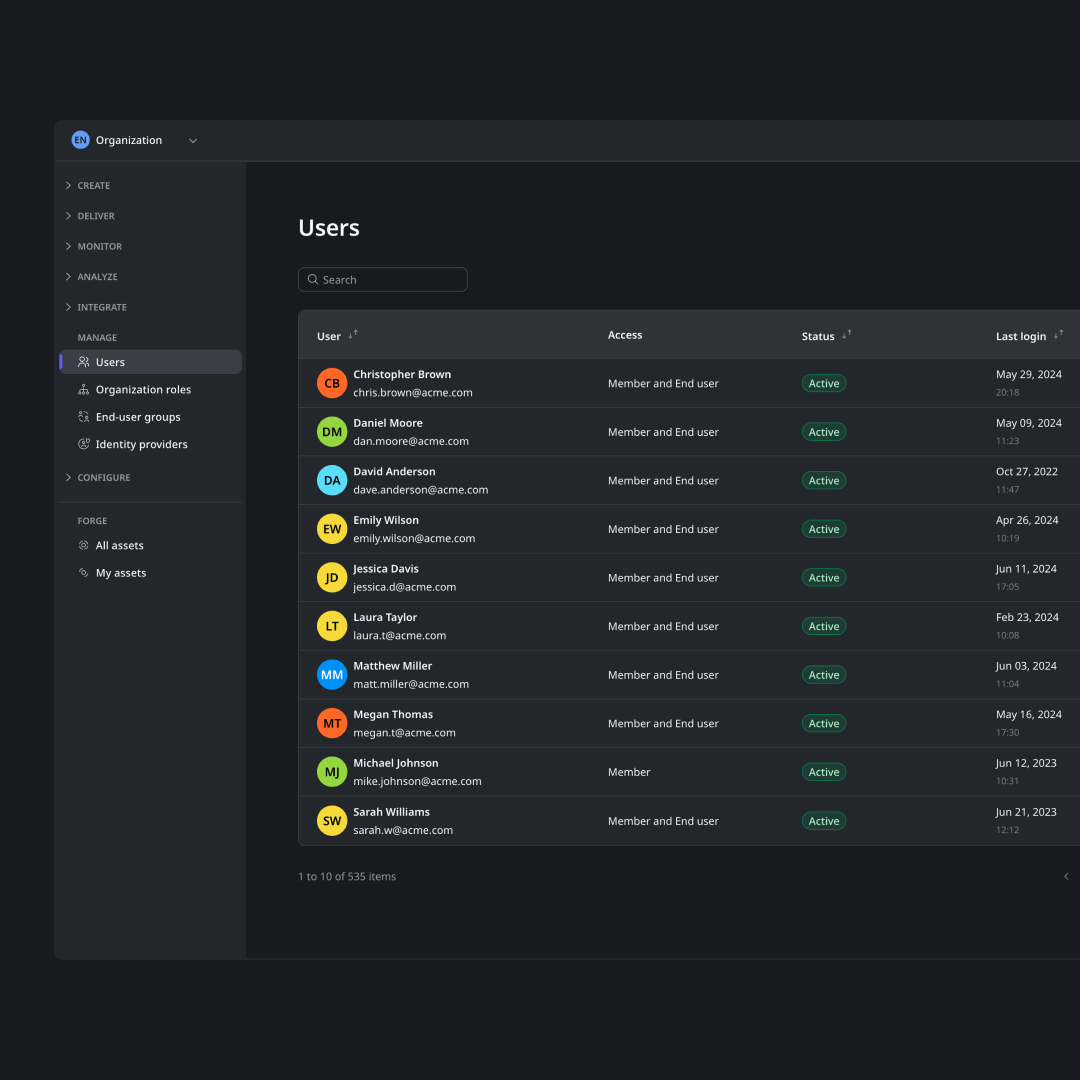
エンタープライズレベルの高度なセキュリティを実装
他のAIプラットフォームと違い、OutSystemsはアプリのセキュリティに一切の妥協をしません。基準を満たすだけでなく、基準を上回る、エンタープライズレベルの保護を提供します。

セキュリティパッチの自動適用やゼロダウンタイムにより、手作業を排除してユーザーエクスペリエンスを強化
CI/CDツールとアプリ保護機能を統合して、セキュアなモバイルアプリを開発
オンプレミス、プライベートクラウド、パブリッククラウドなど、あらゆる自社インフラにOutSystems Private Gateway経由でアプリケーションを簡単かつセキュアに接続
複数の可用性ゾーン(AZ)にわたるフェイルオーバーであらゆる事態に対処

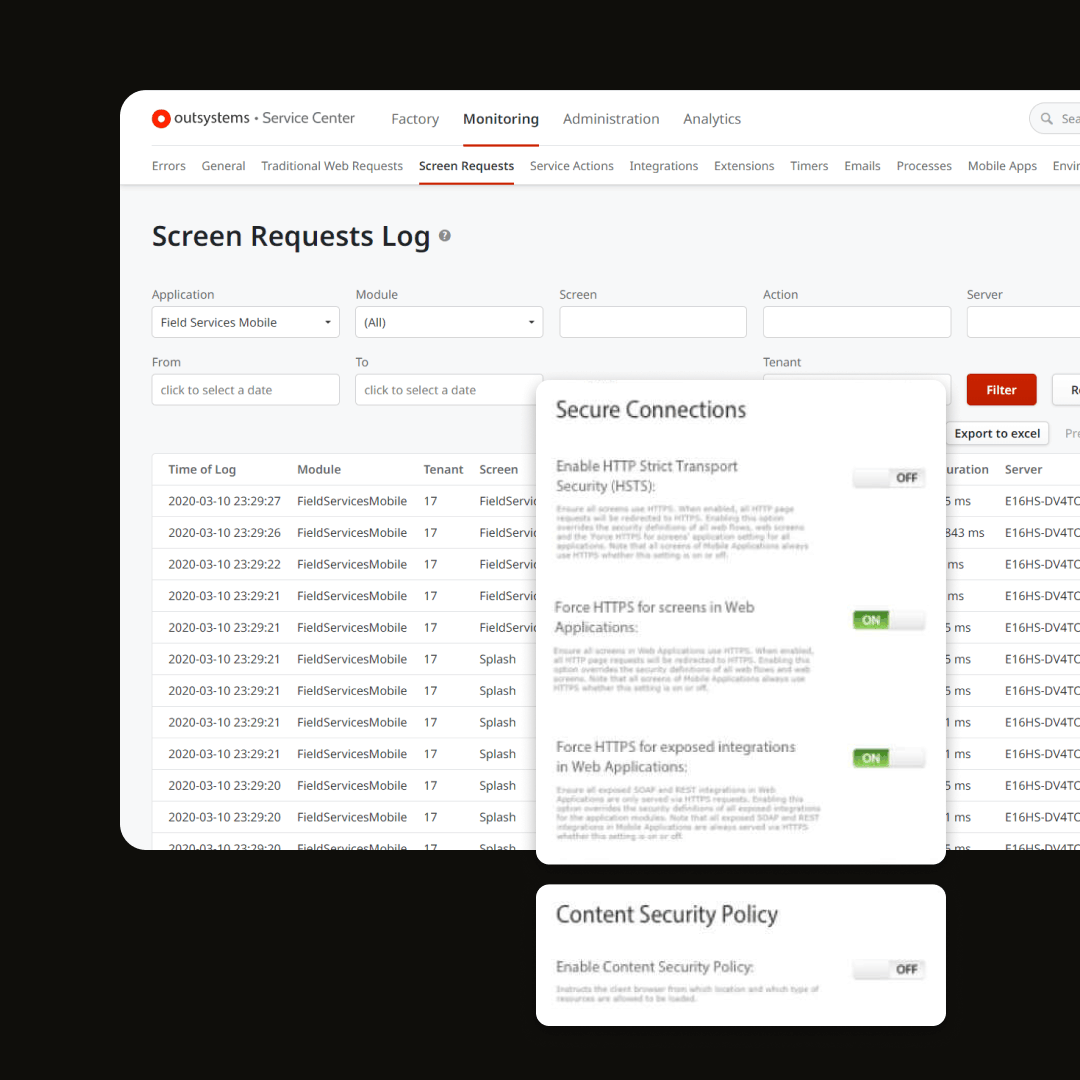
卓越したプラットフォームとネットワークのセキュリティ
サイバー脅威に単独で取り組む必要はありません。OutSystemsにはエンタープライズレベルのプラットフォームとネットワークセキュリティが標準で組み込まれているため、リスクの高い作業の多くを任せることができます。
業界をリードするWebアプリケーションファイアウォール(WAF)により、SQLインジェクションやXSSに対する最高水準の保護を実現
コンテンツ配信ネットワーク(CDN)を活用し、自社のWebアプリケーションファイアウォールとOutSystemsのWAFを組み合わせることで、DDoS攻撃を阻止
継続的な自動侵入検知、マルウェアのスキャン、実行時の完全性監視により、想定外のアクティビティや潜在的な脅威を検出・防止
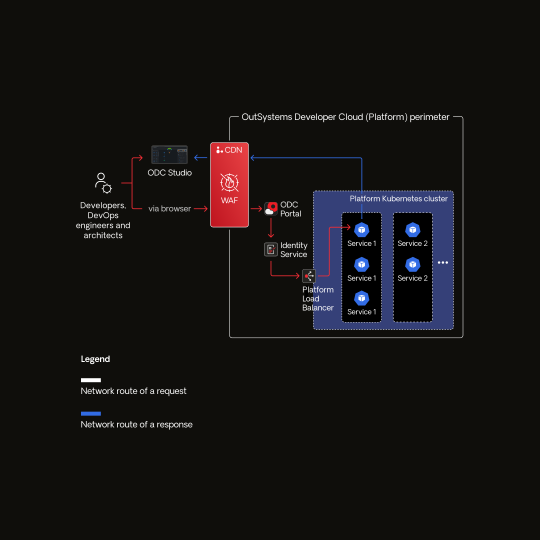
ミッションクリティカルなアプリケーションのセキュリティ
自社のアプリには、ミッションクリティカルなアプリケーションにふさわしいレベルの強固なセキュリティが求められます。OutSystemsが提供するのは、まさにそのようなセキュリティです。
直感的なビジュアルIDEと自動化されたSDLC(ソフトウェア開発ライフサイクル)により、脆弱性の原因となる設定ミスを防止
IPアドレスに基づいてユーザーアクセスを選択的に許可/ブロックする機能により、OutSystemsアプリケーションとネットワークトラフィックを確実に管理
本番、開発、QAのランタイムを分離することでリスクを最小化

セキュアでないデータ運用を防止するための砦
データは、ユーザーにとって最も重要なアセットのひとつです。だからこそ、OutSystemsでは、故意または過失によるデータ損失、データ漏洩、不正なデータ使用を防止するために必要な保護レイヤーを提供しています。
迅速な復元を可能にする継続的な増分バックアップによりデータ損失を回避
開発ステージごとに専用のデータベースを配置することで、ヒューマンエラーや内部関係者による脅威のリスクを低減
送信中や保存中のデータの暗号化と、標準装備の暗号化ツールで、卓越したデータ保護を実現

制限のないアクセス制御
アプリの開発者、利用者、利用方法を完全に制御して、シャドーITやその他の深刻な事態の発生を防ぎましょう。
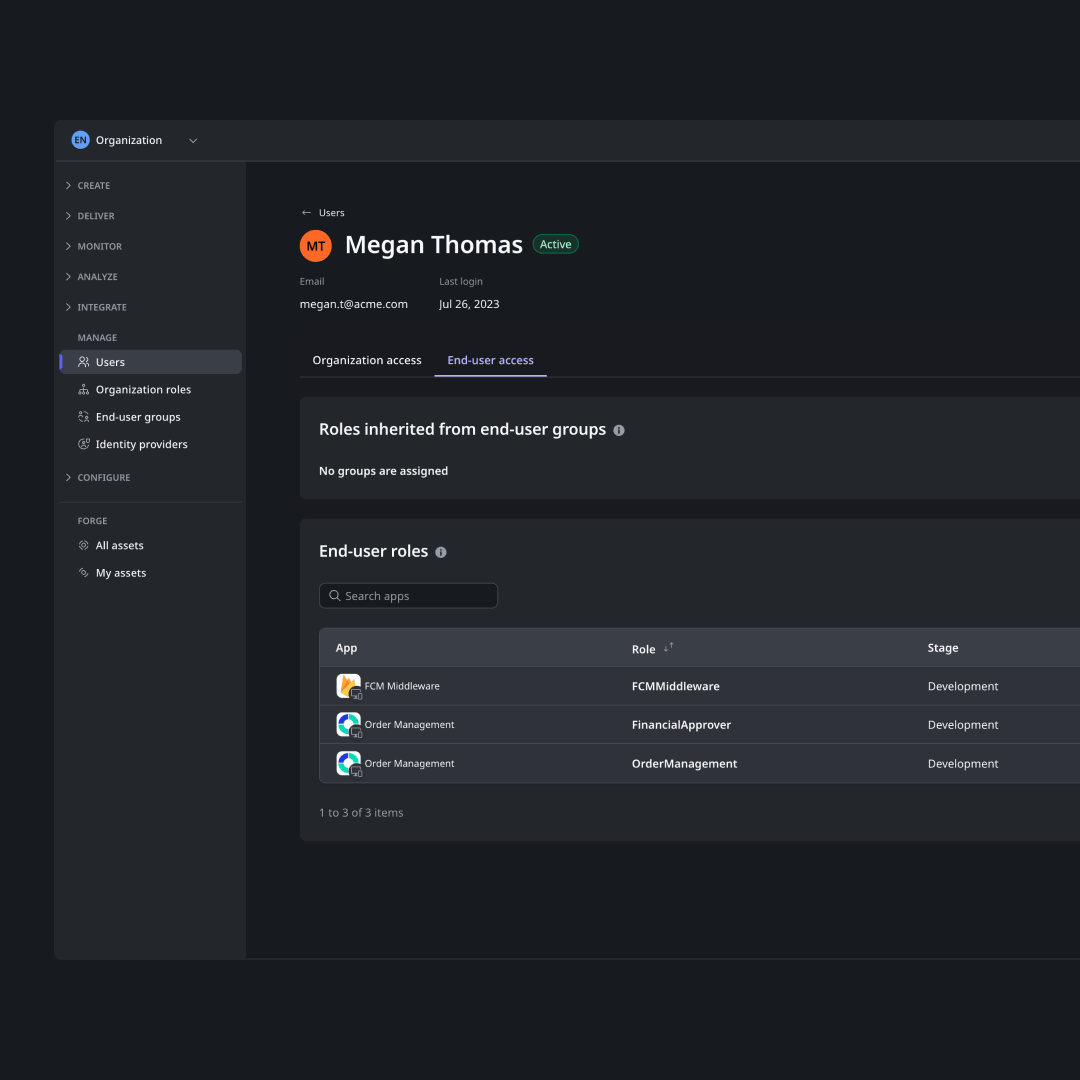
自社のガバナンスモデルやアクセス管理戦略に合わせてカスタマイズされた柔軟なセルフマネージドのID・アクセス管理で、攻撃者の浸入経路を遮断
最小権限の原則を適用して、可能な限り厳格な認可と認証の基準を維持
ビルトインIDプロバイダを利用するか、独自のIDプロバイダをシームレスに統合する(BYOP)かを選択可能
国内外のコンプライアンス基準に適合
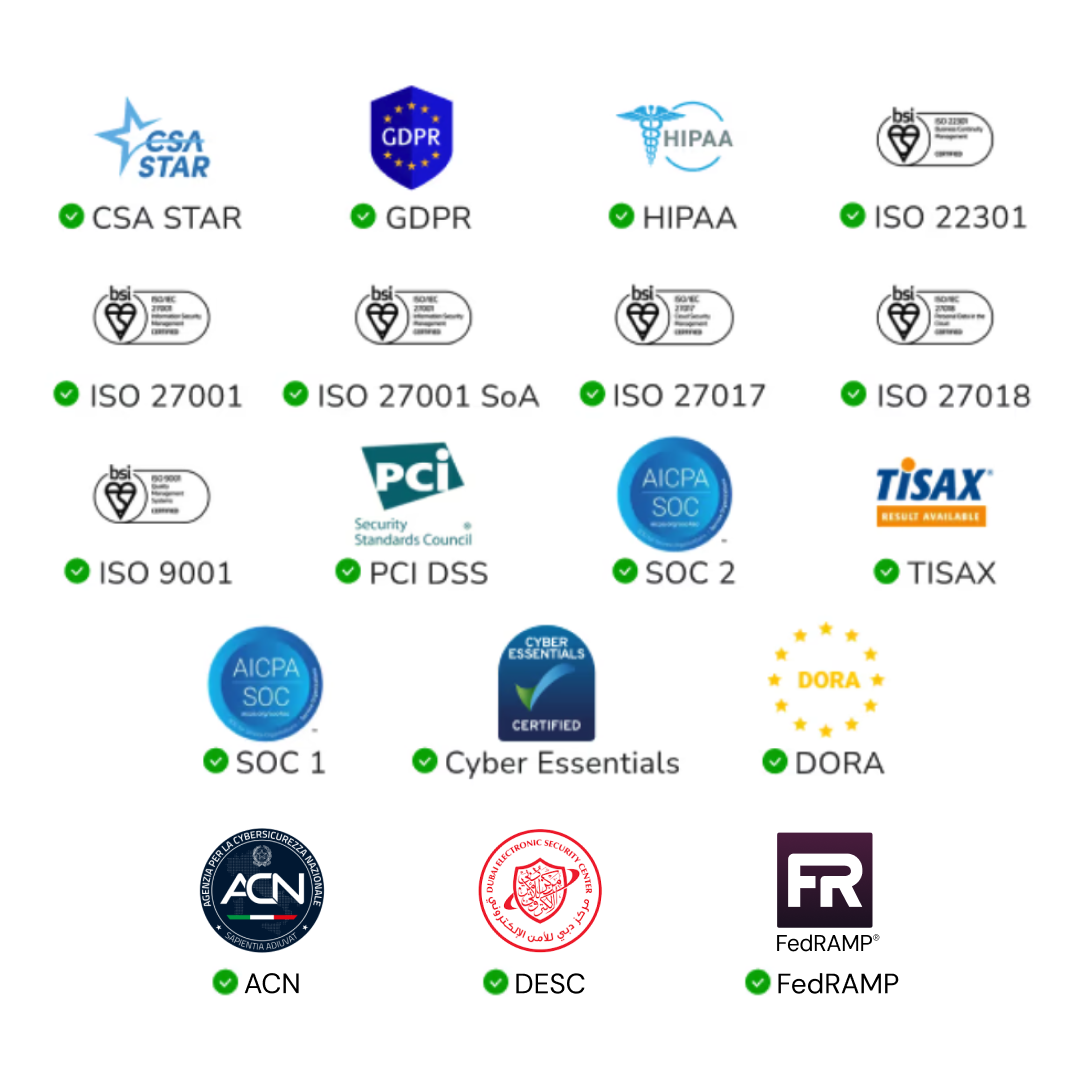
OutSystemsプラットフォームは、厳格なコンプライアンスプログラムにより、国内外の業界や政府が定めたインフラの整合性、データ保護、規制対応に関する厳格な要件に対応しています。
ENS(スペイン)、ACN(イタリア)、DESC(UAE)をはじめとする各国の基準に適合した、FedRAMP認証済みのプラットフォームが盤石な基盤となり、安心感のある開発を実現
進化するEU規制やグローバル規制(GDPR、EUデータ法、EU AI法など)のほか、HIPAA、PCI DSSといったプライバシー・業界要件を継続的に遵守
Security FAQ
OutSystems platforms comply with HIPAA, PCI DSS, and FedRAMP requirements and hold certifications including SOC 2 Type II and multiple ISO standards. Built-in security and governance controls help customers build compliant applications out of the box. OutSystems also complies with privacy laws such as GDPR. See the OutSystems Trust Center for current details.
OutSystems can support HIPAA-regulated use cases for healthcare organizations and teams handling protected health information. Depending on the deployment model and customer requirements, OutSystems can support Business Associate Agreements and security controls for access, encryption, monitoring, and governance. Customers should confirm scope, responsibilities, and configuration requirements during compliance review.
OutSystems supports government and public sector use cases. The OutSystems platform is also FedRAMP-Moderate Authorized in a partnership with Knox.
OutSystems supports enterprise authentication methods, including SAML, OAuth, SSO, Microsoft Entra ID, formerly Azure AD, and multi-factor authentication via supported identity providers. The platform also includes accelerators for social/B2C logins (Facebook, Google, LinkedIn, Apple). This allows organizations to centralize access control, align applications with existing identity standards, and enforce consistent login and security policies on the platform and across applications.
OutSystems supports centralized user provisioning, role-based access control, and permission management across applications. Teams can define roles, assign access by user or group, and manage permissions as their application portfolio grows. OutSystems also allows customers to extend the built-in capabilities via user and access management REST APIs. This helps enforce least-privilege access, simplify administration, address specific provisioning and role management scenarios, and maintain governance across multiple applications and teams.
OutSystems encrypts data at rest by default and protects data in transit with TLS. Depending on the platform and deployment model, physical and logical separation and namespace segregation help keep customer data isolated. Included security libraries also support envelope encryption, allowing customers to add a second layer of protection for sensitive data.
Data residency depends on the customer’s selected region. OutSystems can support region-specific hosting requirements so organizations can keep application data in approved geographies. This is especially important for regulated industries with sovereignty, privacy, or country-specific compliance obligations.
OutSystems manages platform and infrastructure patching based on the deployment model. In ODC, one-click patching (1CP) reduces application-owner effort: customers are notified when patches are available, and the platform automatically builds and applies them the next time the application is published.
Yes. Customers can perform penetration testing on OutSystems applications, typically with coordination and approval to ensure testing follows platform policies and does not disrupt shared infrastructure. Security teams can also use third-party scanning tools and internal assessment processes to validate application security, compliance requirements, and production readiness.
During a Vendor Risk Assessment, OutSystems provides security documentation, compliance evidence, architecture details, data protection information, and responses to customer security questionnaires. Procurement, legal, and security teams use this process to evaluate risk, confirm controls, and verify that OutSystems meets organizational requirements before purchase or deployment.
Yes. OutSystems can integrate with security monitoring and observability tools such as Splunk, Dynatrace, New Relic, and SIEM or APM platforms. Teams can stream logs, monitor application behavior, and connect platform events to existing security operations workflows, helping maintain visibility across the broader enterprise monitoring stack.
OutSystems includes built-in monitoring capabilities for application health, errors, performance, access activity, and operational events. Teams can use native logs and dashboards to investigate issues, detect abnormal behavior, and support audits. For deeper observability, OutSystems can also connect with external monitoring, SIEM, or APM tools.
OutSystems helps protect sensitive data in AI use cases through agent guardrails, access controls, governed model connections, data boundaries, auditability, and configuration options that limit what information agents or AI features can use. Customers should define approved models, data handling rules, and review workflows to reduce leakage risk.
OutSystems supports AI security guardrails such as role-based access, governed tool access, monitoring, audit logs, and controls that help reduce risks like prompt injection, PII exposure, and unsafe outputs. Agent Evaluations also let teams test agent behavior against defined datasets and criteria, helping validate that agents perform as expected before and after deployment.
AI processing location depends on the selected model, provider, and deployment architecture. OutSystems can support governance patterns that help customers choose approved models, route requests through controlled endpoints, and align processing with regional or data sovereignty requirements. Teams with strict constraints should validate provider, hosting, and data residency options early.
関連リソース

モバイルアプリのセキュリティ | 評価ガイド


Sentry

攻撃対象領域を減らすためのベストプラクティス

クラウドネイティブのセキュアなローコードプラットフォームを実現するためのチェックリスト